

Agentic AI Pindrop Anonybit
I Got a Call From “My Bank” Last Month — And It Wasn’t My Bank. Here’s What Pindrop, Anonybit, and Agentic AI Are Actually Doing About It
So this happened to my dad, not me, but I ended up in the middle of it anyway.
He got a call that sounded exactly like someone from his bank’s fraud department. Same tone, same script structure you’d expect, mentioned a “suspicious wire transfer” that needed verifying. He almost gave up his PIN over the phone before he called me, confused, asking if this was normal. Agentic AI Pindrop Anonybit
It wasn’t a person. Or rather — it was a cloned voice running through an automated script, and it was good enough that a 68-year-old who’s pretty sharp about scams almost fell for it. That’s when I went down a rabbit hole trying to understand how banks and call centers are supposed to be catching this stuff in 2026, because clearly the old “does the voice sound weird” test is dead.
That’s how I landed on this combo you’ll start seeing mentioned a lot if you work anywhere near fraud prevention, customer support tech, or contact center infrastructure: Agentic AI + Pindrop + Anonybit. It sounds like buzzword soup the first time you hear it. It isn’t. Let me break down what it actually means, because I spent a few weeks reading vendor docs, security reports, and talking to a friend who works in fraud ops at a mid-size credit union to actually understand it.
Why This Suddenly Matters (It’s Not Hype)
Here’s the number that actually stopped me: contact centers are now getting hit with a fraud attempt roughly every 46 seconds. Voice cloning used to require studio-quality audio and real effort. Now someone can grab ten seconds of your voice from a podcast, a voicemail greeting, or a company earnings call and generate something convincing enough to fool a tired agent on a Friday night shift.
Deepfake voice attempts have exploded over the past couple of years — we’re talking well over 1,000% growth, hitting banking, insurance, and retail call centers hardest. My credit union friend told me their fraud team went from occasionally flagging a weird call to dealing with cloned-voice attempts on a near-daily basis. Agentic AI Pindrop Anonybit
The scary part isn’t even the voice cloning itself. It’s that a lot of these attacks are automated end to end now. A bot dials the IVR, answers security questions using stolen personal info, navigates the phone tree, and reaches a live agent — no human fraudster sitting there dialing. That’s the “agentic” part of the problem, and it’s why the defense had to get agentic too.
Breaking Down What Each Piece Actually Does
I kept getting confused reading about this because articles throw around “Pindrop,” “Anonybit,” and “agentic AI” like everyone already knows how they connect. Here’s the plain version.
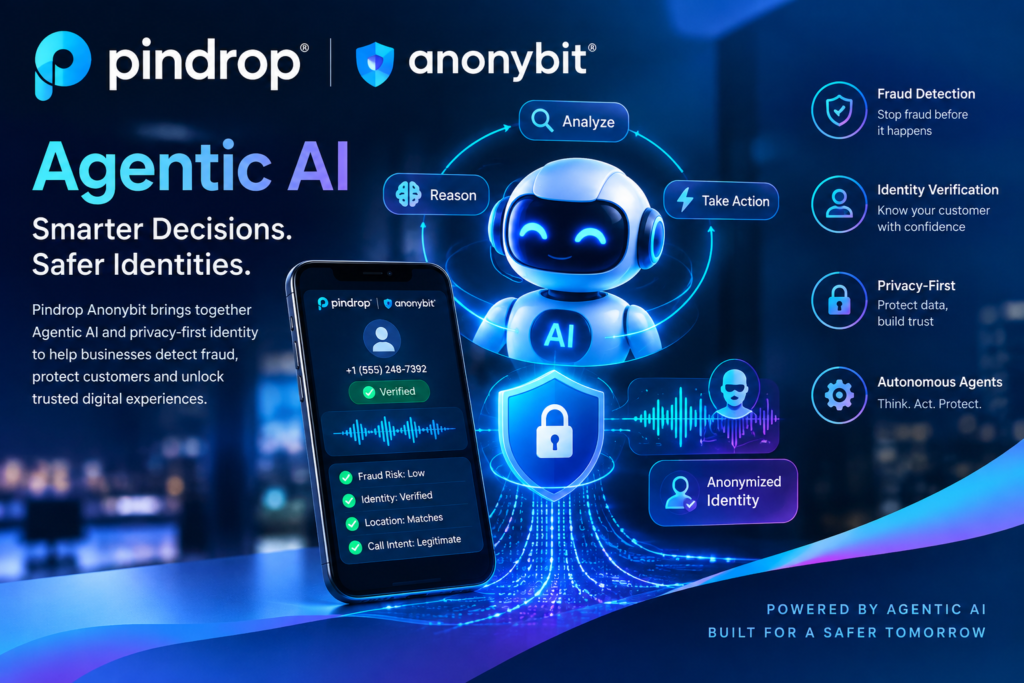
Pindrop is the ear. It listens to the call in real time and checks the audio itself — not what’s being said, but the actual sound waves — for signs it was machine-generated rather than a real human voice. Think of it like a lie detector for the audio signal, not the person. Pindrop’s been doing this a long time (they’ve analyzed billions of calls at this point) and they plug into systems companies already use, like Amazon Connect, Genesys, Cisco Webex, and Five9. That last part matters — a bank doesn’t have to rip out its whole phone system to add this.
Anonybit is the vault, except there’s no vault. This one took me a minute to wrap my head around. Instead of storing your voiceprint or fingerprint in one central database (which is basically a giant “hack me” sign for criminals), Anonybit splits the biometric data into pieces and scatters them. No single breach can expose a complete identity because no single place holds the complete identity. You can change a password after a breach. You can’t change your voice or your face, so this “nothing to steal in one place” approach makes a lot more sense the longer you think about it.
Agentic AI is the decision-maker. This is the part that ties it together. Instead of a dumb rule like “if the fraud score is above X, block the call,” the agentic layer looks at everything at once — the Pindrop liveness score, the Anonybit match confidence, what device is being used, whether the location matches past behavior, how large the transaction is — and makes a judgment call in real time. A slightly off voice score paired with a familiar device and a small transfer might just get logged quietly. That same score paired with a brand-new device and a big wire transfer triggers an immediate hold or a request for extra verification.
It’s less like a tripwire and more like a bouncer who’s actually paying attention to the whole room, not just checking one ID at the door. Agentic AI Pindrop Anonybit
How This Plays Out in a Real Attack (Walking Through It)
My credit union friend walked me through a version of this that actually happened on their systems, and it stuck with me because it’s less abstract than reading a vendor whitepaper.
- The call comes in. An automated bot, using a cloned voice built from a few seconds of audio scraped online, dials the bank’s IVR at 2 a.m.
- Pindrop flags it almost instantly. The voice liveness detection catches artifacts in the audio — things a human ear wouldn’t notice but the acoustic analysis picks up — and raises a risk flag within seconds.
- The agentic layer weighs the full picture. It’s not just the voice flag. It checks: is this device known? Does the location match past calls? Is the request unusually large? All of that gets combined instead of treated as separate checkboxes.
- Anonybit confirms there’s no legitimate match. Even if the voice sounded convincing, there’s no valid biometric match sitting behind it because the real customer’s data isn’t stored the way the attacker assumes.
- The system escalates or blocks — without waiting for a human. By the time a fraud analyst might have looked at it manually, the call’s already been held or the transaction stopped.
The whole verification cycle in systems that have this fully deployed reportedly runs under 200 milliseconds. That’s faster than you’d notice as a customer, which is honestly the goal — you don’t want legitimate customers sitting through a 10-second awkward pause every time they call.
What I Got Wrong At First
I initially assumed this was just “better spam filtering for phone calls,” like a caller-ID blocklist but smarter. That’s not it at all. A blocklist approach only works against known bad numbers or known patterns — it’s reactive. This stack is designed for attacks it’s never seen before, because it’s not matching against a list, it’s analyzing the actual physics of the audio and the behavior pattern of the session.
I also assumed the biometric privacy angle was just marketing fluff — “we care about your privacy” boilerplate that every company slaps on their site. Turns out it’s actually a legal and compliance issue too. If a company stores a full biometric database and it gets breached, that’s a much bigger regulatory headache under privacy laws than a password leak. Splitting the data so no single record exists isn’t just nice-to-have, it changes what a company even has to disclose if something goes wrong.
Steps If You’re Evaluating This for Your Own Business
If you’re on the operations or fraud-prevention side and someone just told you to “look into this,” here’s roughly how I’d approach it based on what I’ve read and heard: Agentic AI Pindrop Anonybit
- Check your existing call center platform first. If you’re on Genesys, Five9, Amazon Connect, or similar, integration is a much smaller lift since these tools were built to plug in rather than replace.
- Ask vendors for actual accuracy numbers, not just marketing claims. Look for reported real-world accuracy rates and ask how they’re measured — synthetic test data versus live call data can give very different numbers.
- Get your compliance team involved early, especially around biometric data handling. Decentralized storage architectures can genuinely reduce your regulatory exposure, but you still need your own legal review — don’t take a vendor’s word that you’re automatically compliant.
- Start with a pilot on high-risk transaction types — wire transfers, password resets, large withdrawals — before rolling it across every call type. That’s what most of the case studies I found describe as the actual rollout pattern.
- Train your human agents on what a flag actually means. A risk score isn’t a verdict. Agents still need clear guidance on when to escalate versus when the system’s already handled it.
Common Mistakes People Make Talking About This Stuff
I saw this a lot while researching: people treat “agentic AI” as if it’s one single product you buy, when it’s really more of an approach or a layer that sits on top of detection tools like Pindrop and identity tools like Anonybit. It’s not a plug-and-play app — it’s an architecture.
The other mistake is assuming voice cloning detection alone solves the problem. It doesn’t. A convincing fake voice paired with stolen personal information can still get pretty far if there’s no layer checking device behavior, transaction context, and biometric matching all together. The value here really is in the combination, not any single piece.
And honestly, the biggest mistake — the one my dad almost made — is assuming that if a voice sounds right, it must be a real person. That instinct is going to keep getting less reliable, not more. Which is exactly why this shift toward acoustic analysis and layered, automated decision-making is happening in the first place. Agentic AI Pindrop Anonybit
Final Thoughts
None of this stuff is bulletproof, and anyone telling you a security system is “unhackable” is selling you something. What this Pindrop-Anonybit-agentic AI combination actually offers is a system that adapts faster than static rules and doesn’t leave a single juicy target sitting in a database somewhere.
For my dad, the fix was simpler and much less technical: he just hung up and called the bank back on the number printed on his card. That’s still the best advice for regular people. But knowing what’s happening behind the scenes at the institutions we trust with our money made me a lot less annoyed the next time a bank call asked me three extra verification questions. There’s usually a reason for the friction now, even when it’s mildly inconvenient in the moment.
Leave a Reply